
OT CybersecurityFrom processto boardroom.
- Process
- Plant floor
- Control room
- Supervisory
- Business
The boardroom
Where decisions about the plant are made, usually without seeing it.
- EmailEvery attack’s favourite front door
- Corporate cloudConnected to more than anyone lists
- ERPPulls numbers from the plant
One click by the right person, and an attacker has a starting point that can lead all the way down.
An OT security strategy the board can endorse, and a view of OT risk in language it can act on.
Explore govern →
Site business
Billing, scheduling and reporting systems that the plant quietly depends on.
- MESTalks to the line every minute
- File sharesDrawings, recipes, passwords
- ReportingReads straight from the historian
It never has to touch a controller. Encrypt the business systems and the operator stops the plant to be safe.
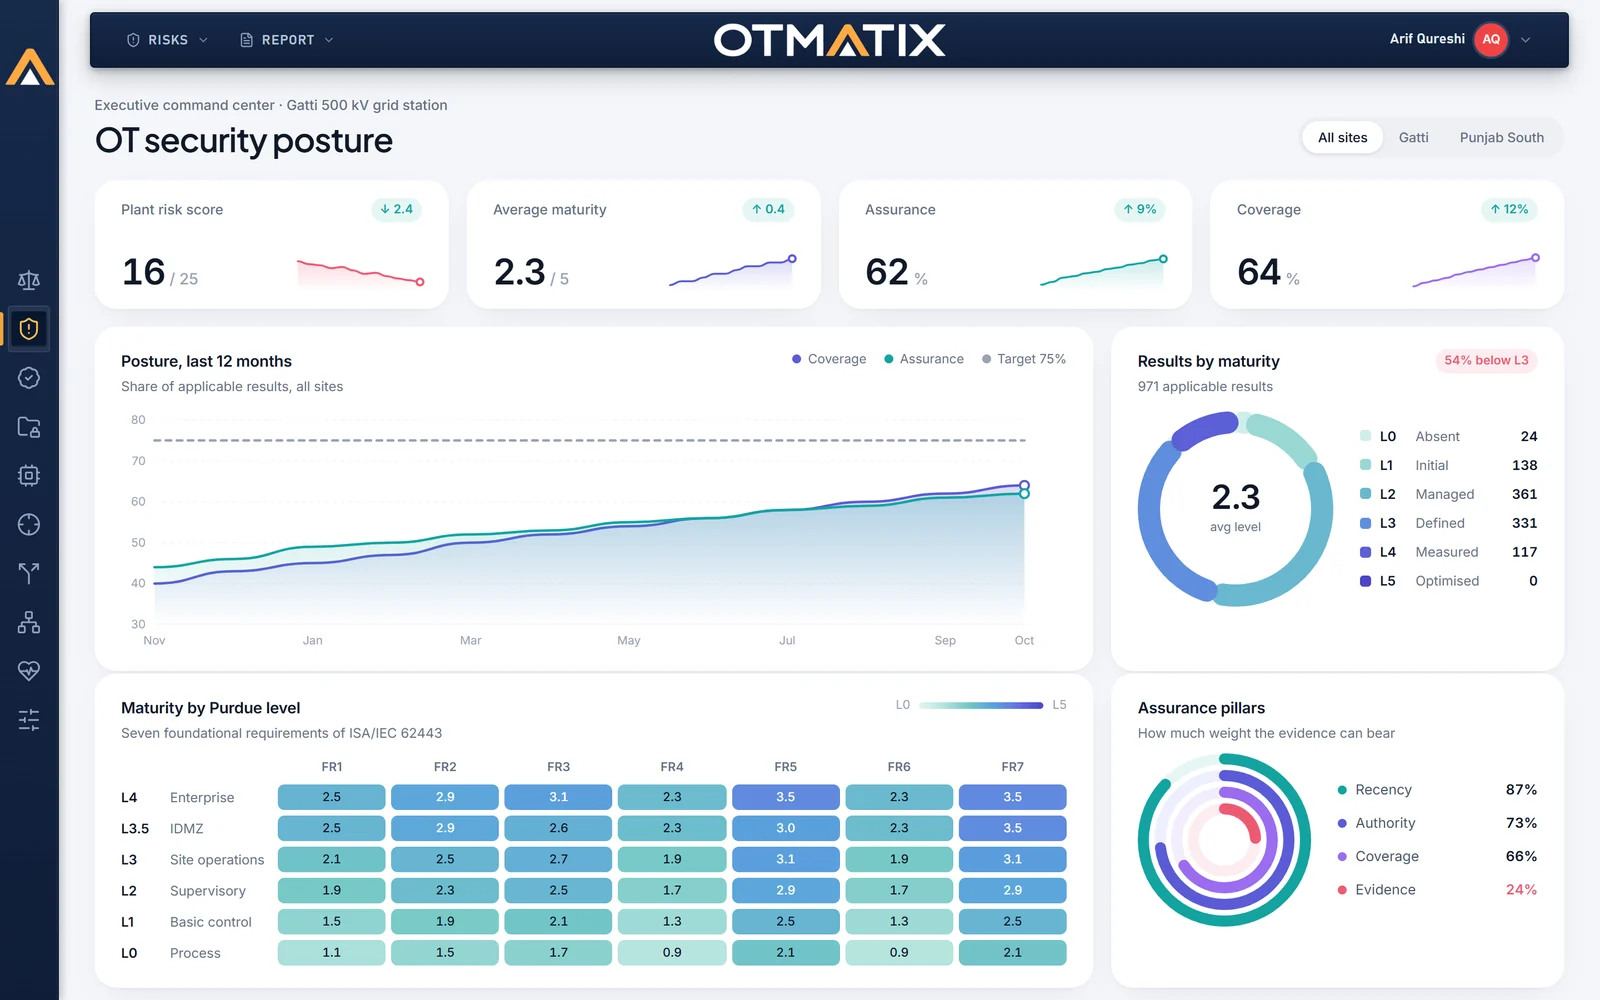
An evidenced posture assessment against all seven IEC 62443 foundational requirements, before anything else.
Explore assess →Ransomware hit the business network. The pipeline was shut down for days as a precaution.
The DMZ
The border between the office and the plant. Or where the border should be.
- Jump serverShared by every vendor
- Patch stagingFiles cross here unchecked
- Remote access gatewayAlways on, just in case
Legitimate remote access that nobody switched off, reachable by anyone who steals the password.
Zones, conduits and a real industrial DMZ, with remote access that is brokered, recorded and time-bound.
Explore design →A satellite network outage cut remote monitoring of 5,800 wind turbines in Europe.
Site operations
Historians and engineering workstations. The keys to every controller live here.
- Engineering laptopCan reprogram any PLC
- HistorianCopies data to corporate
- OT domainShared admin accounts
Isolated plants are rarely as isolated as they look. Contractor laptops and removable media walk straight in.
Hardened golden images, named access instead of shared logins, and patching prioritised by process impact.
Explore protect →The most famous OT attack in history entered here, carried on removable media to engineering workstations.
Supervisory control
The screens operators trust to tell them what the plant is doing.
- Operator HMIWindows XP, still running
- SCADA serverUp for 1,900 days
- Alarm server300 alarms a shift
Someone moves the mouse on an operator screen, and the setpoints start to change.
OT threat detection watched by named senior engineers around the clock, and response plans you have rehearsed.
Explore operate →Remote access to an HMI was used to raise the sodium hydroxide dosing more than a hundredfold. An operator caught it.
Basic control
The controllers that actually open valves, trip breakers and stop the process safely.
- PLCFirmware from 2009
- Safety systemThe last line of defence
- Protection relaySettings decide if faults clear
Protocols here were built on trust. They accept a write or a stop command from anything on the network.
Safety system security where IEC 62443 and IEC 61511 meet, so no cyber event can defeat a safety function.
Explore design →Attackers reached a petrochemical plant’s safety instrumented system, the controller meant to prevent disaster.
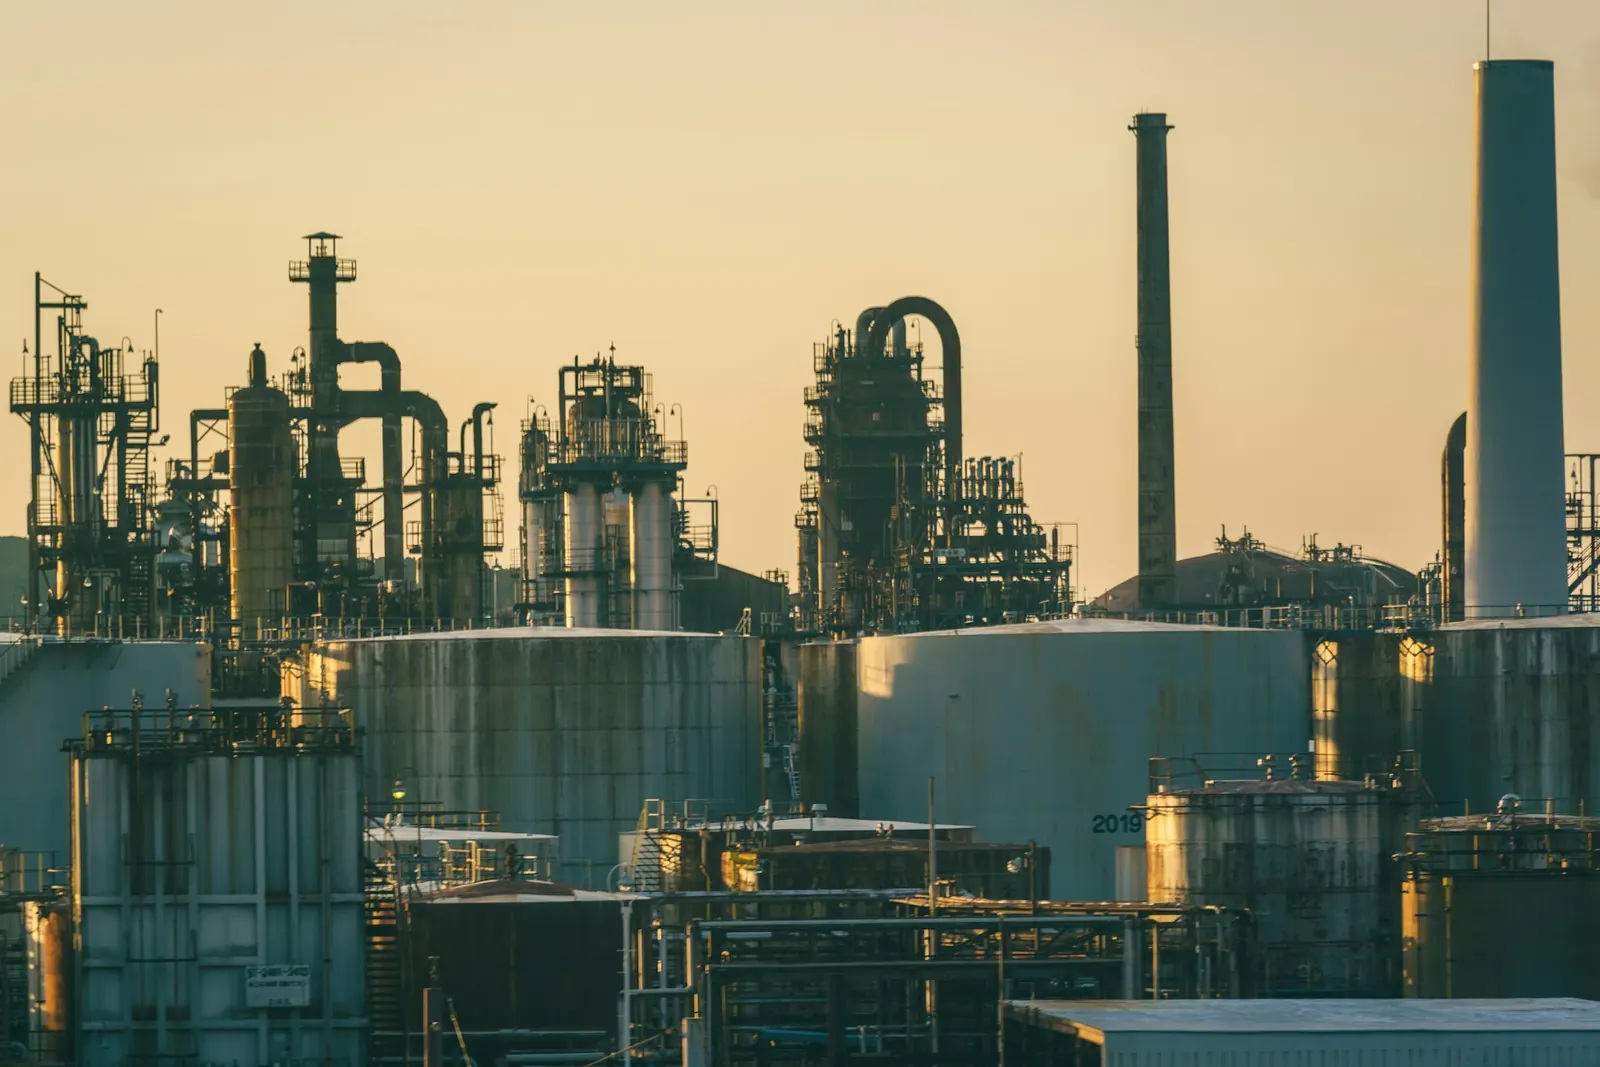
The process
Valves, pumps, sensors and the physical world. Where consequence lives.
- Pressure sensorTrusted without question
- Pump driveSpins what the PLC says
- Temperature loopOne reading from a trip
Change what the instruments report, and every layer above makes the wrong decision with total confidence.
ThePlantWalk: senior practitioners walk this level beside your engineers, device by device, connection by connection.
Explore assess →Seven layers down, the attack that began on a USB stick physically destroyed centrifuges.
Level 0 reached
Most security stops at Level 4.
We start down here.
Then we work our way up, layer by layer, with your engineers beside us and safety holding the final word.
- 06Sustain.
- 05Operate.
- 04Protect.
- 03Govern.
- 02Design.
- 01Assess.
Where do we actually stand, and what could really break the process?
- OT Security Posture Assessment against all seven IEC 62443 Foundational Requirements
- ThePlantWalk
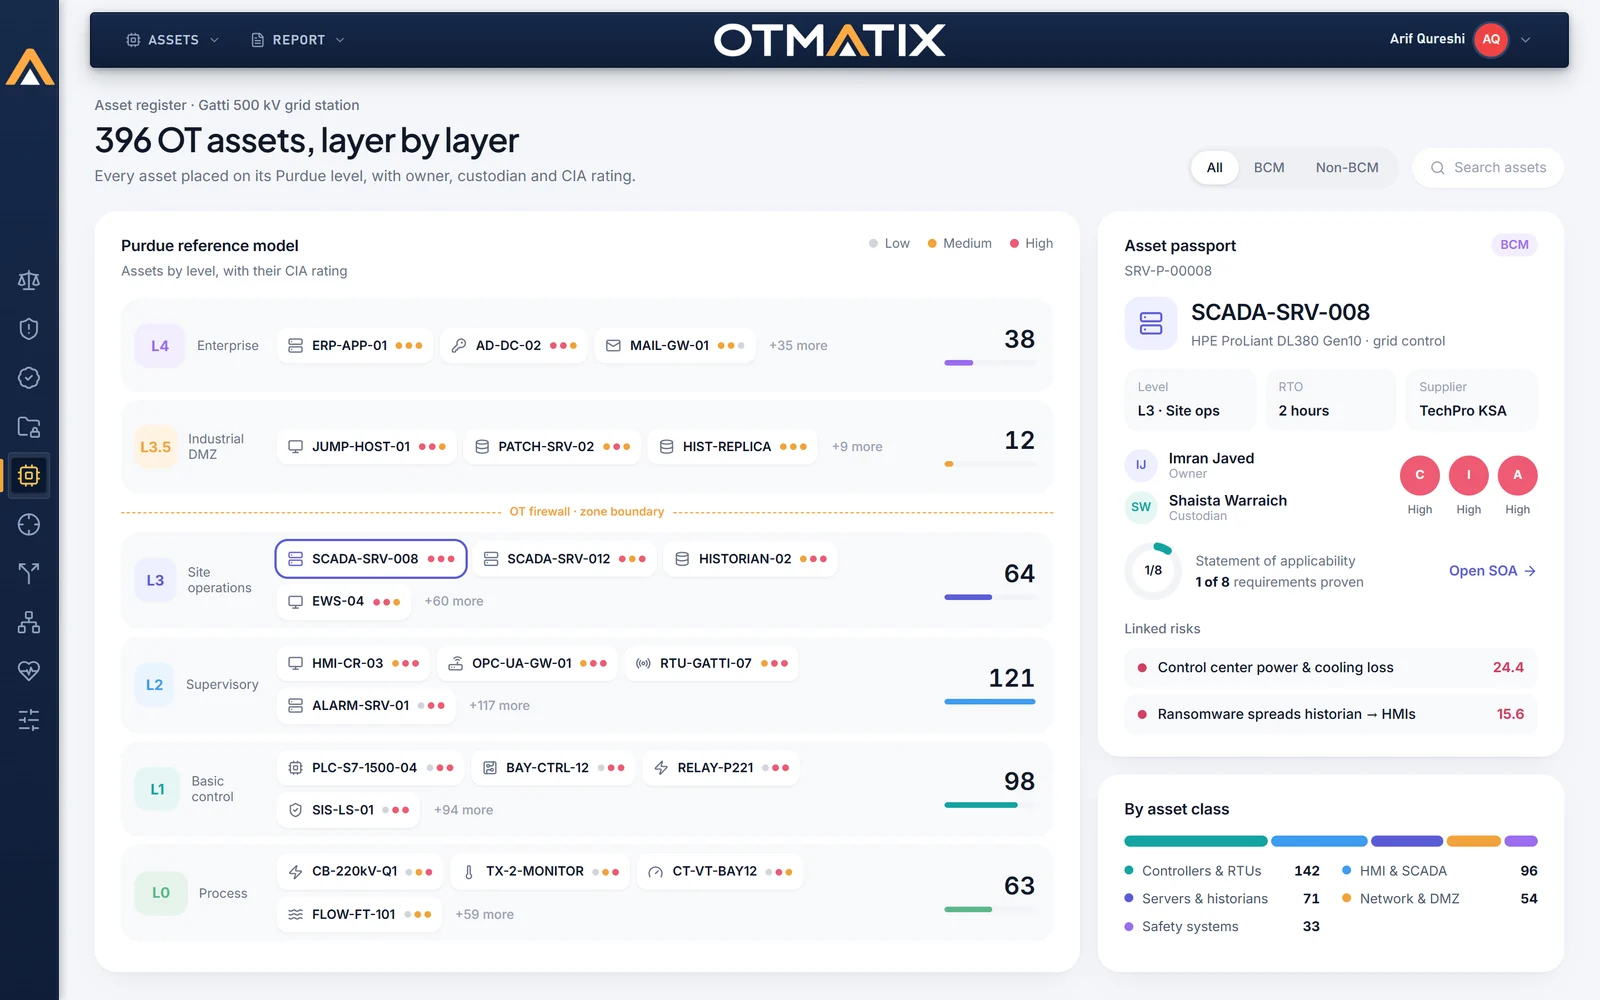
- OT Asset Inventory and Network Visibility
- OT Cyber Risk Assessment
Pure play OT security. Nothing else.
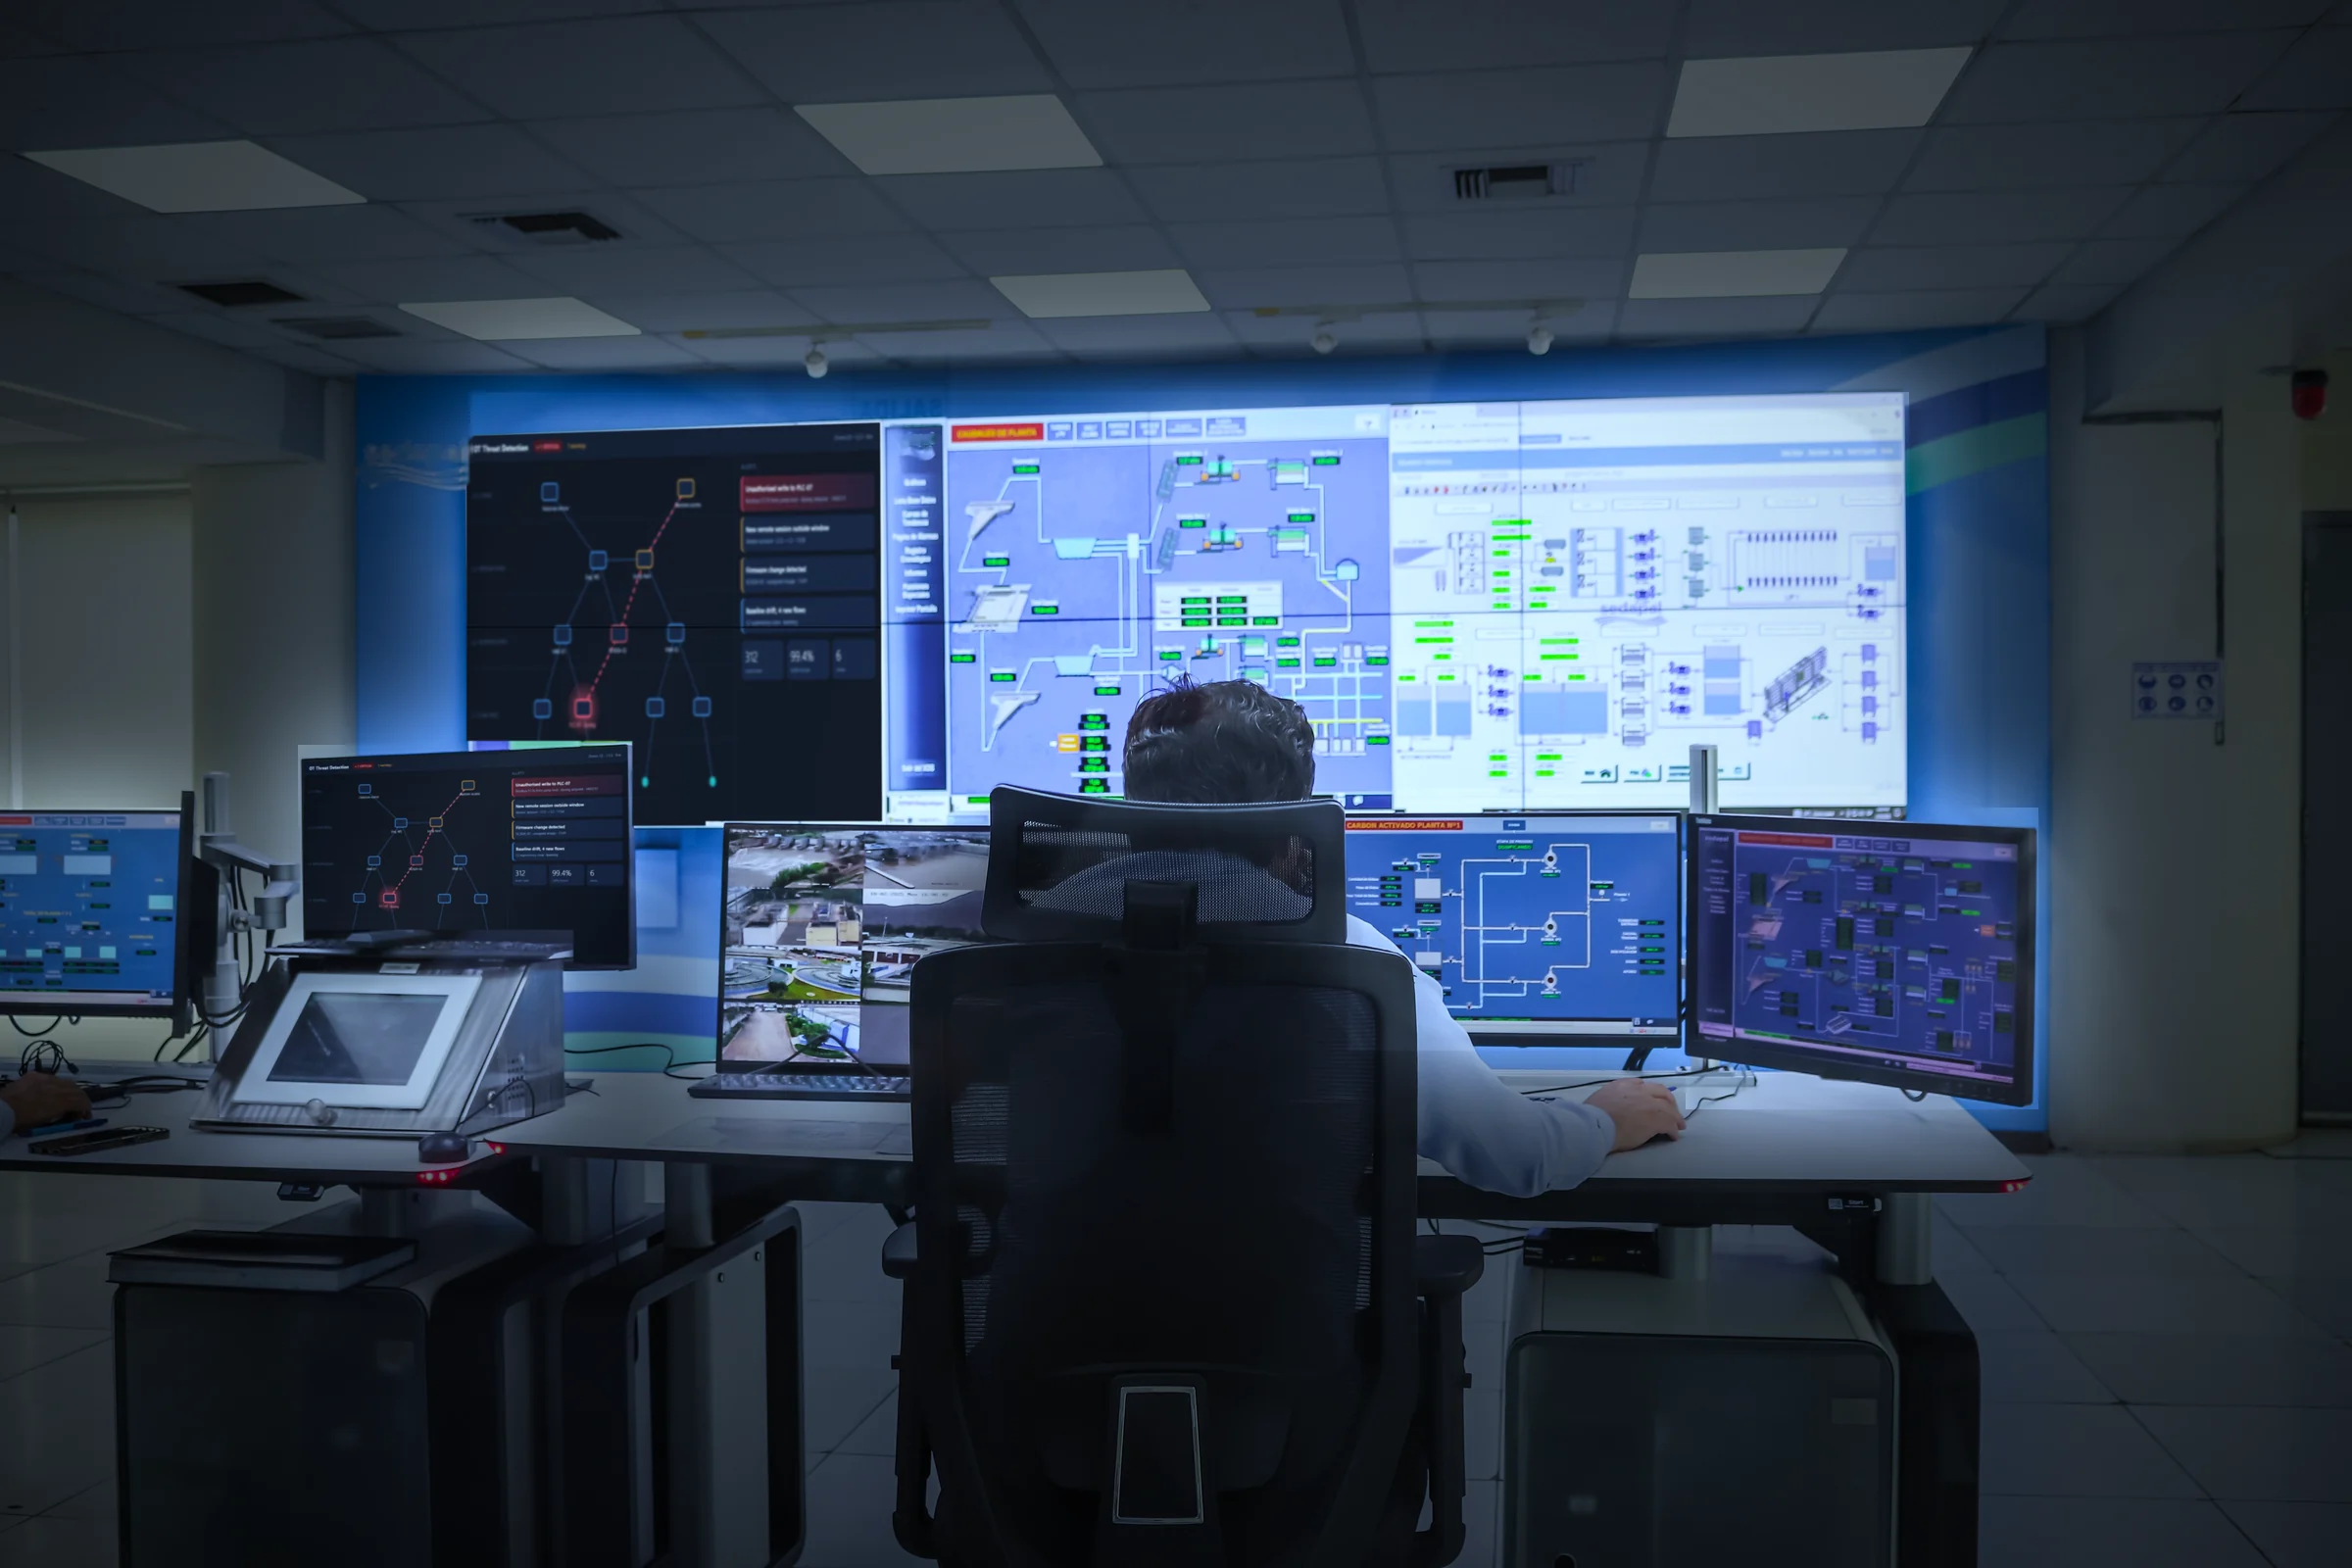
ISA/IEC 62443 Experts, GICSP, CISSP and more, working beside your engineers on site.
OTMATIX
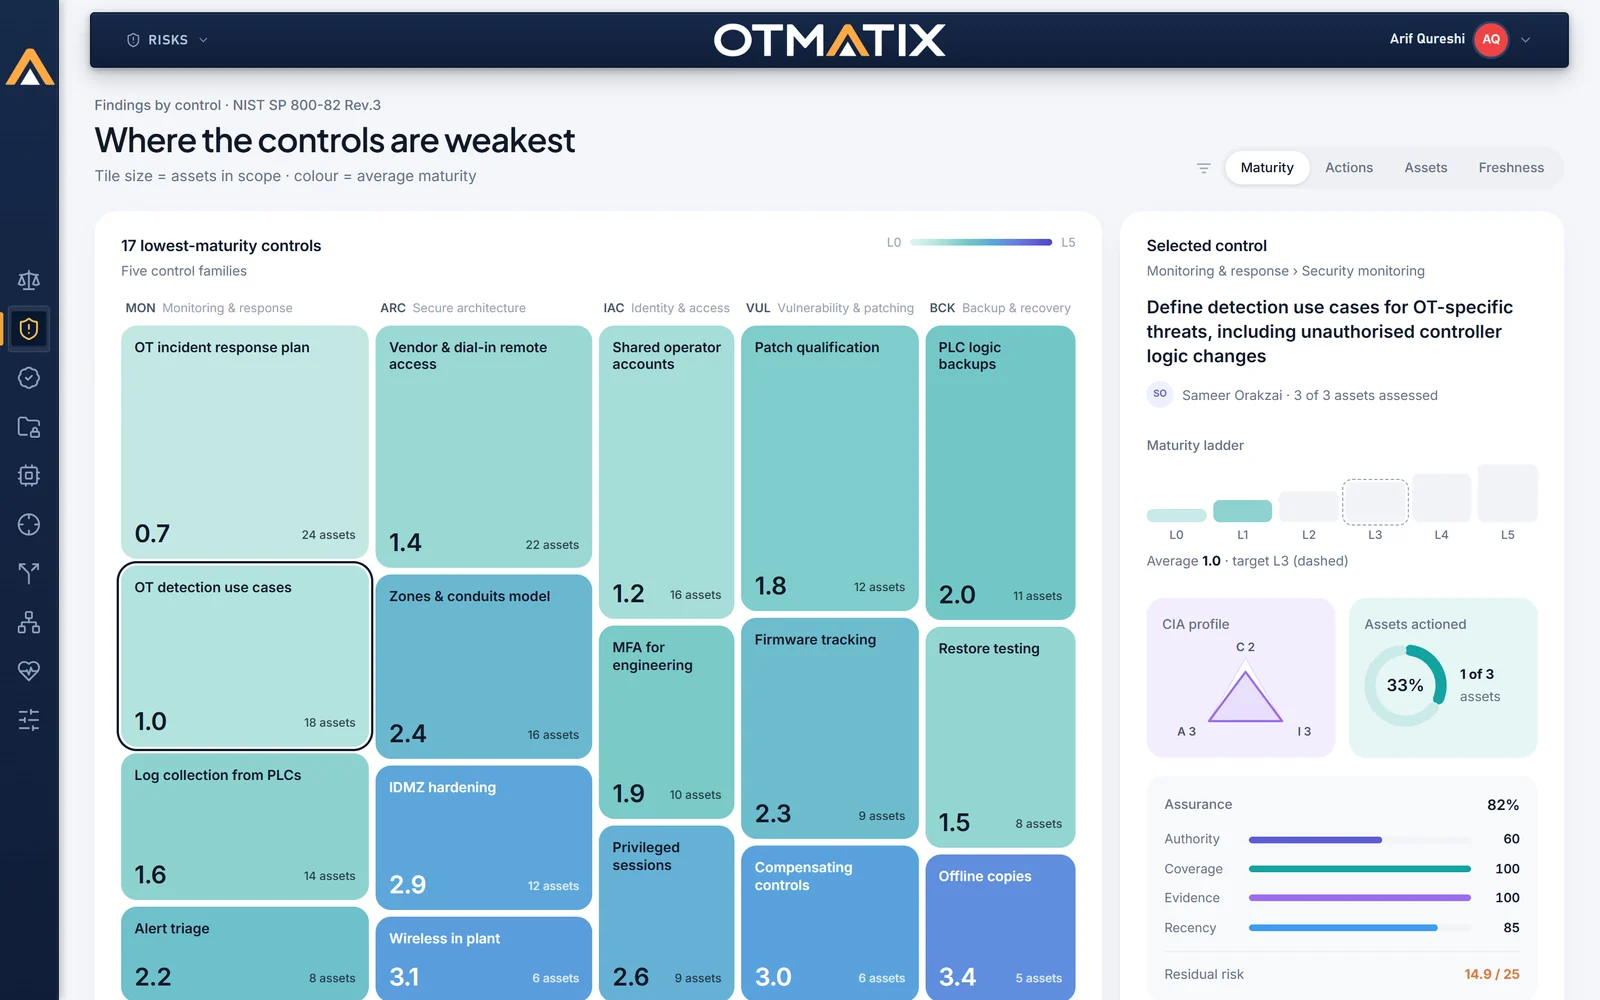
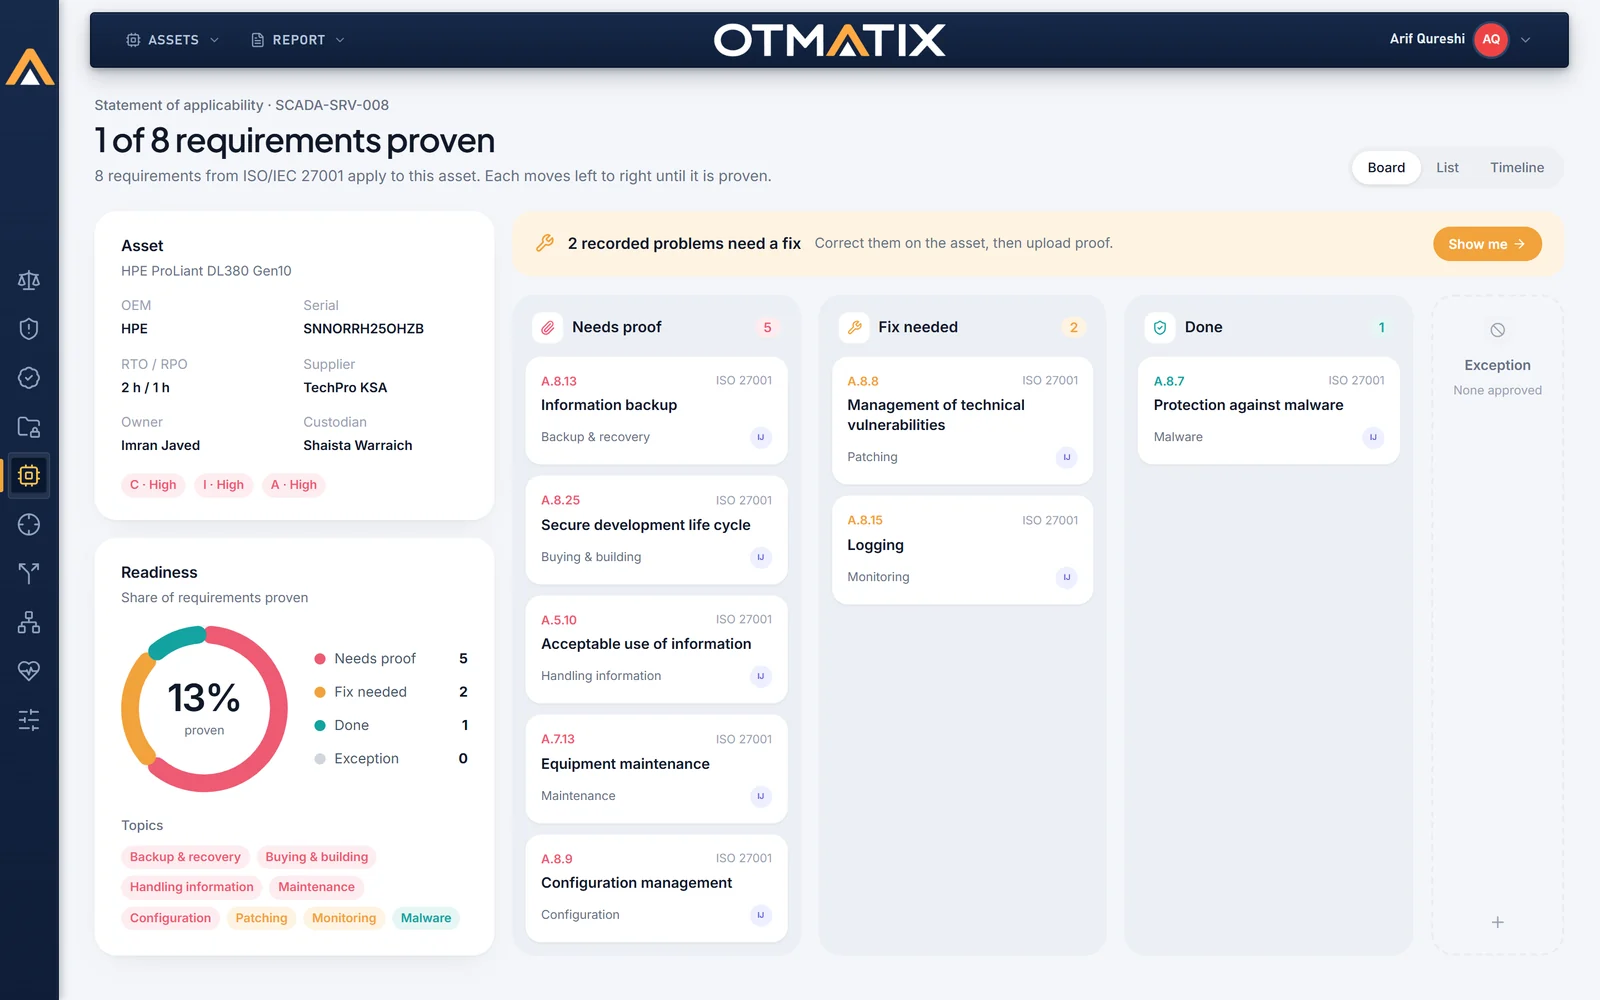
Every finding becomes evidence you keep.
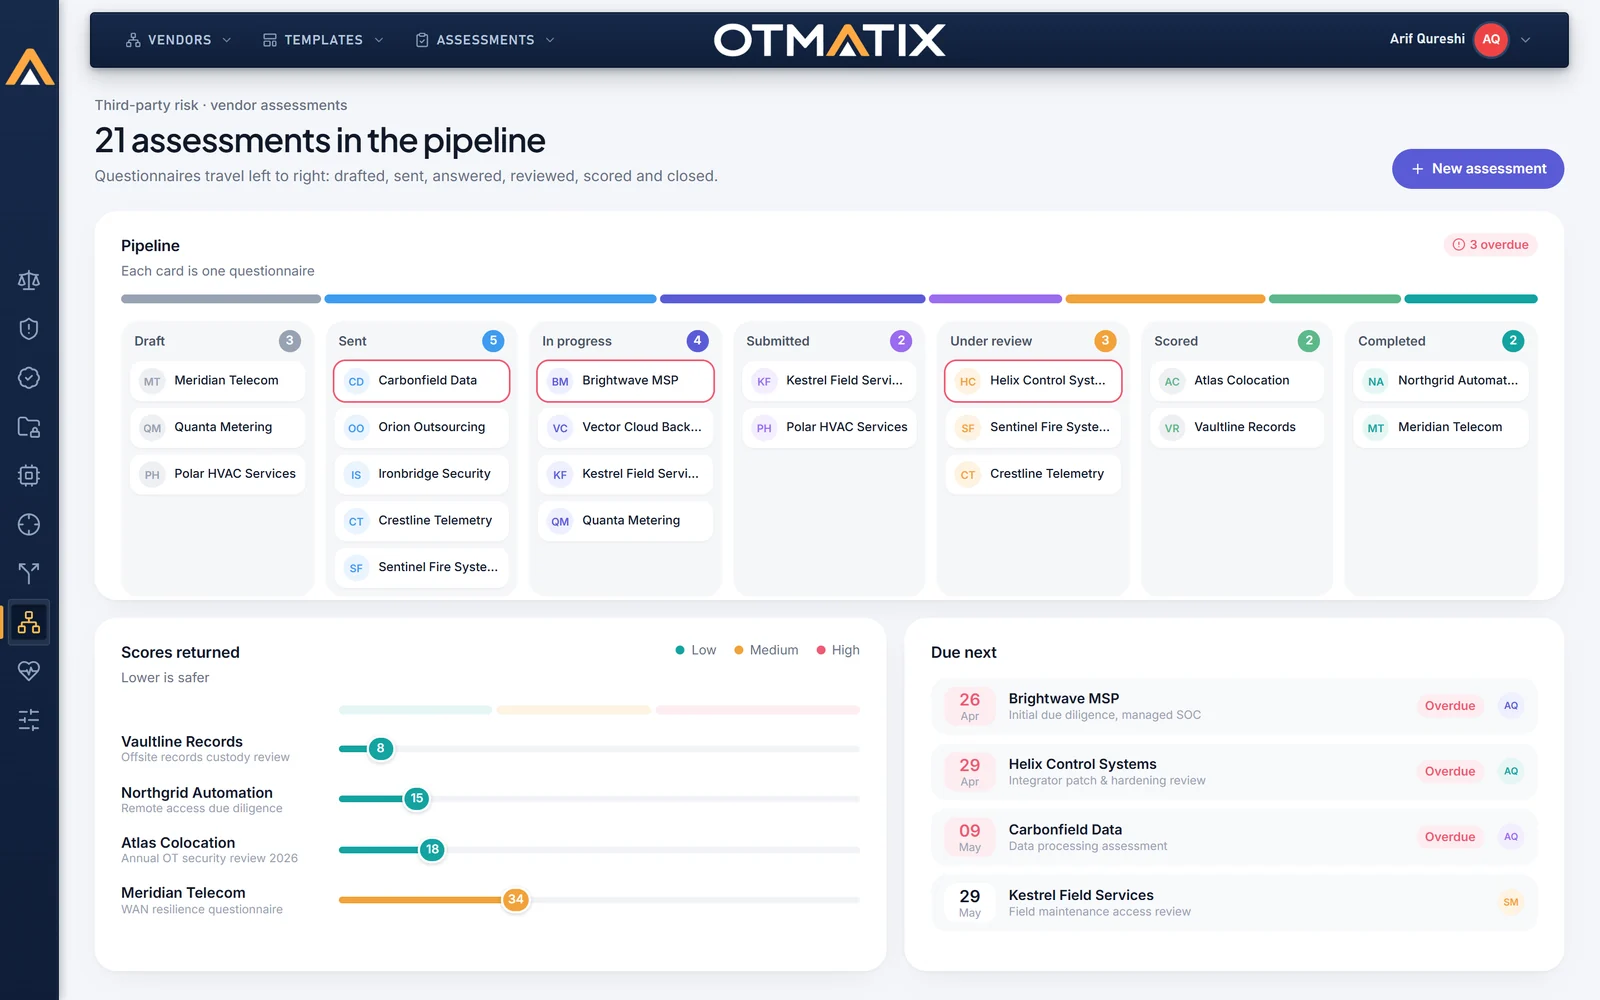
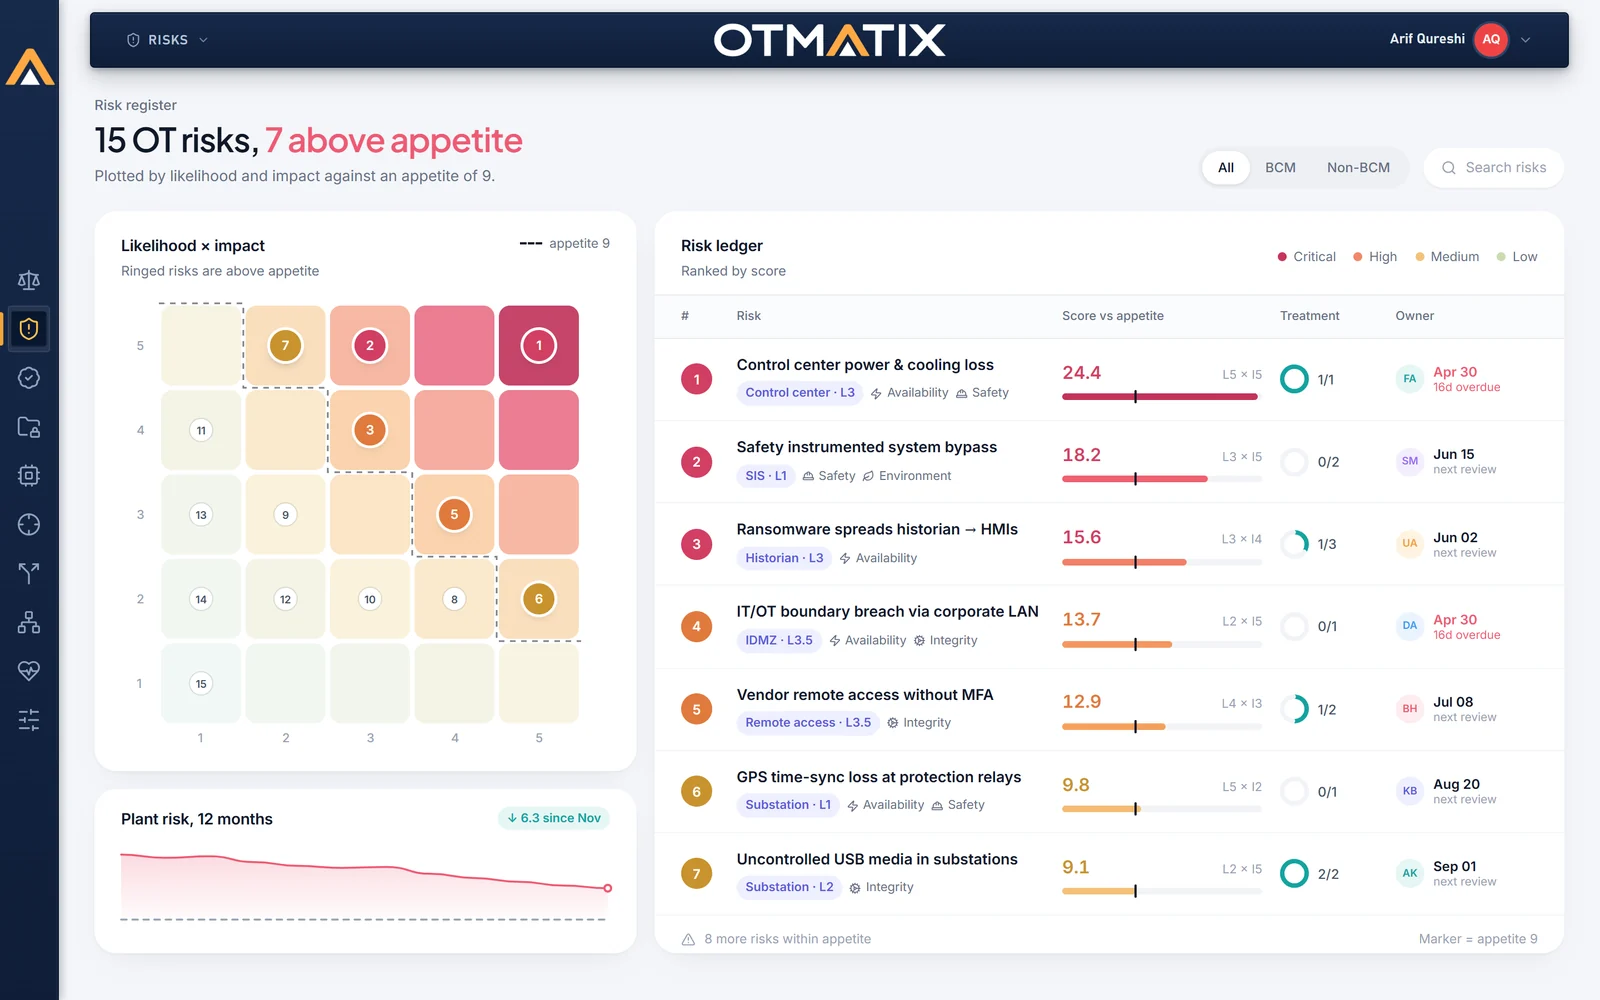
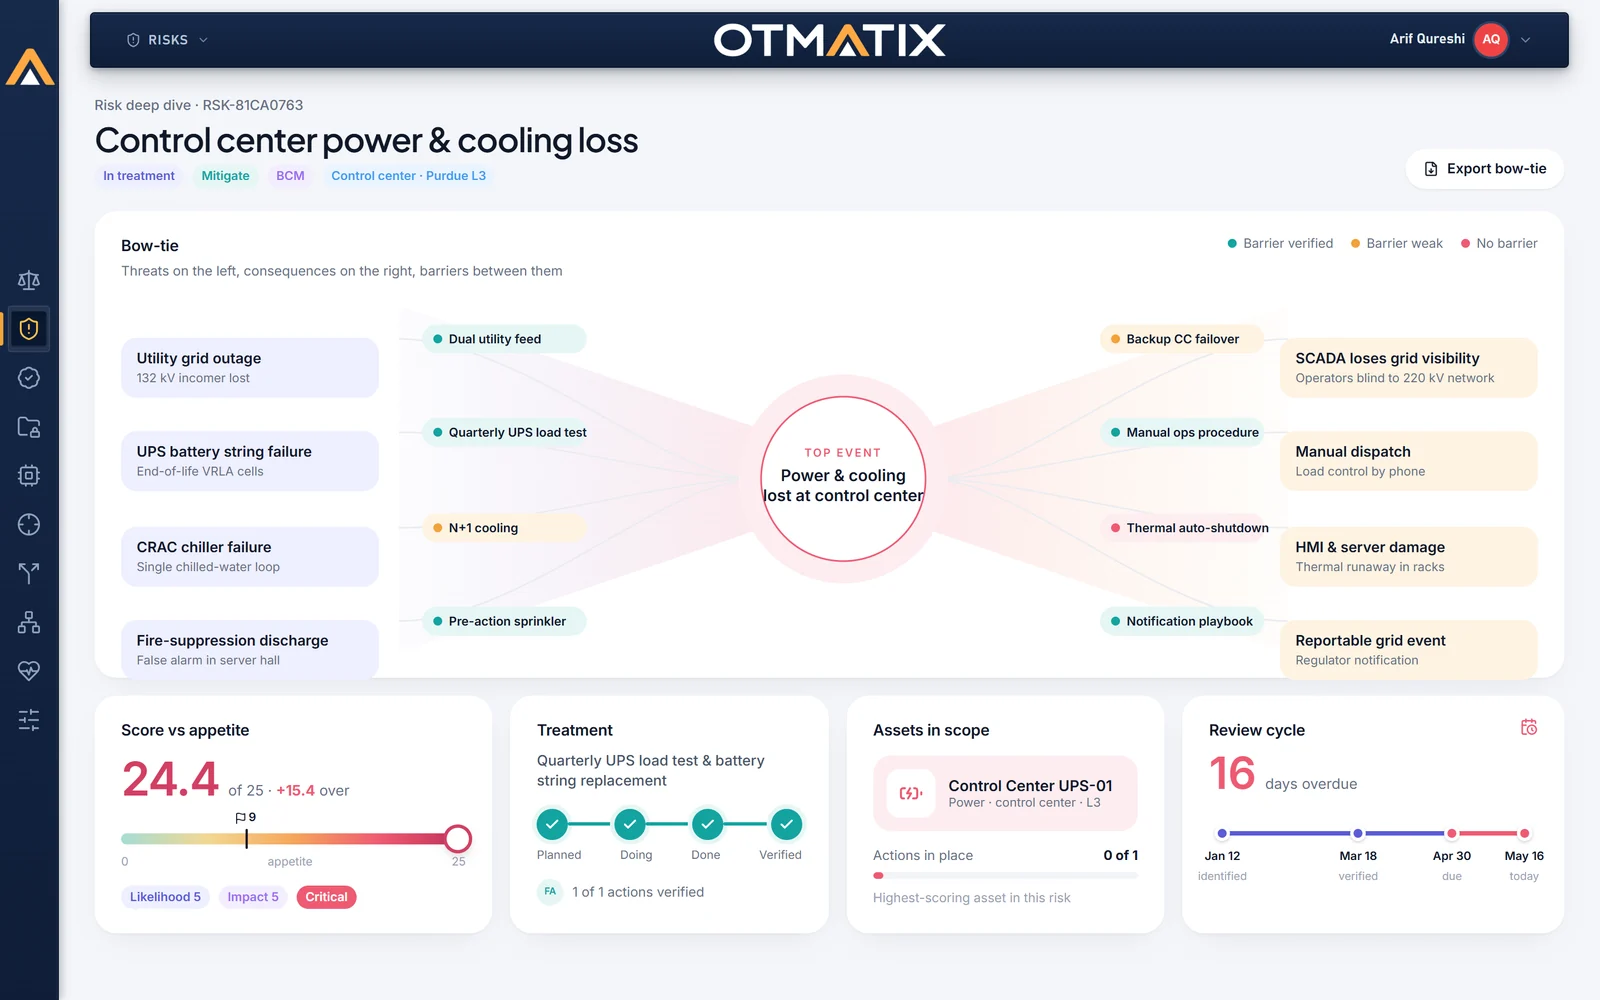
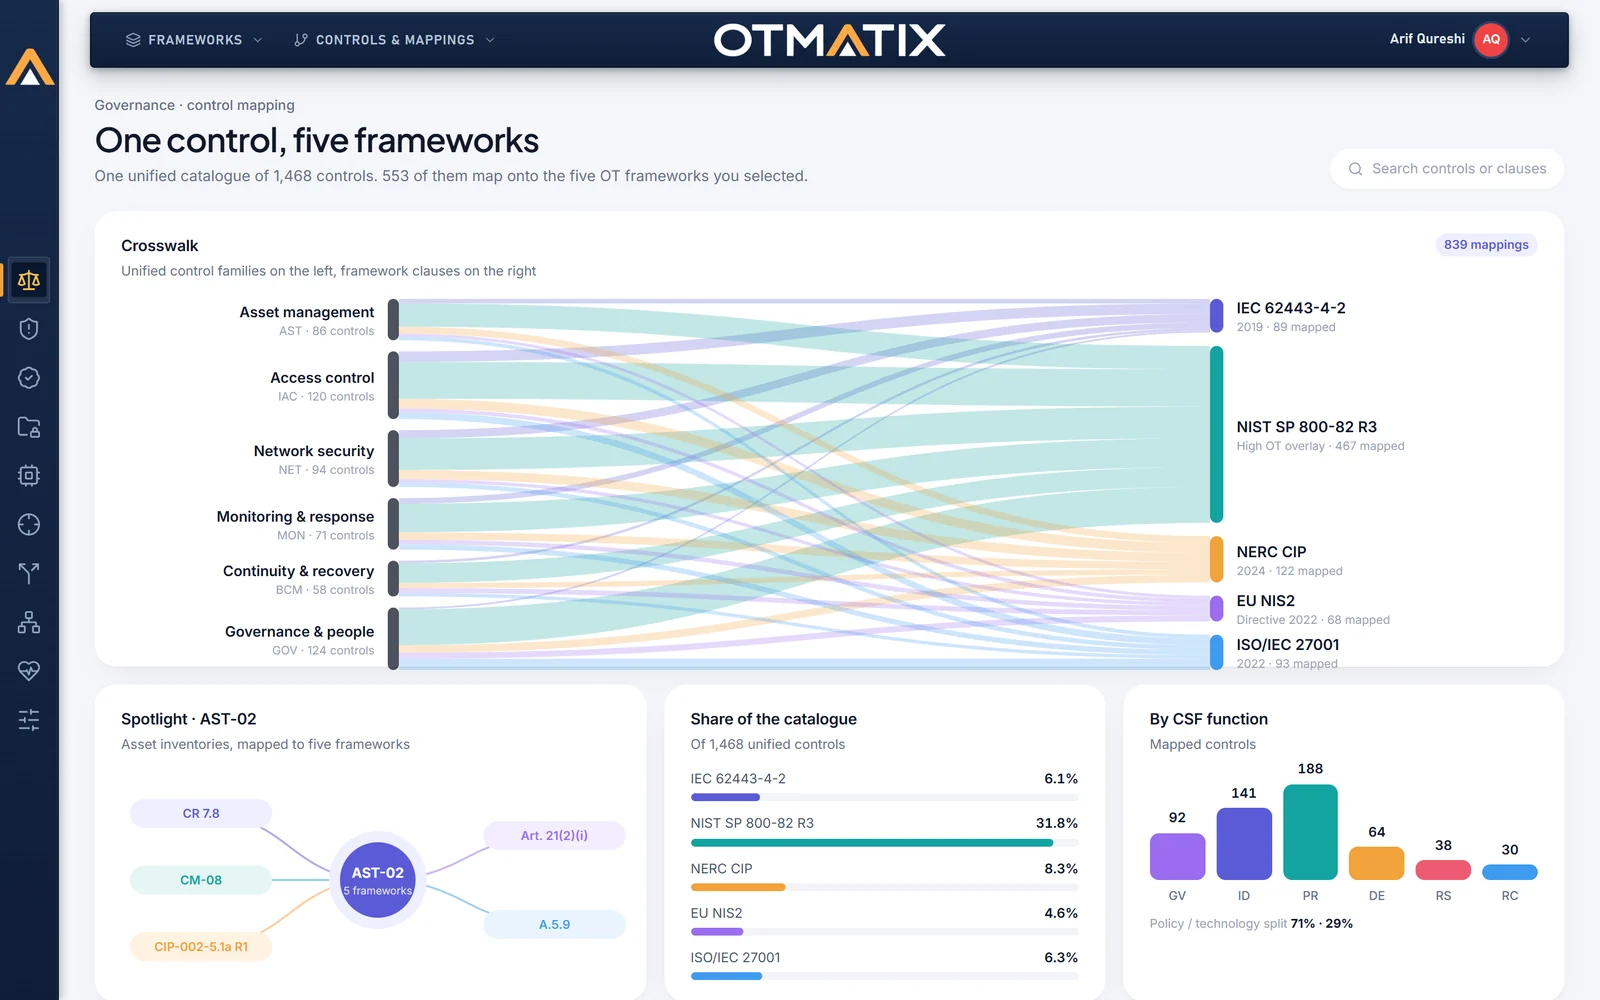
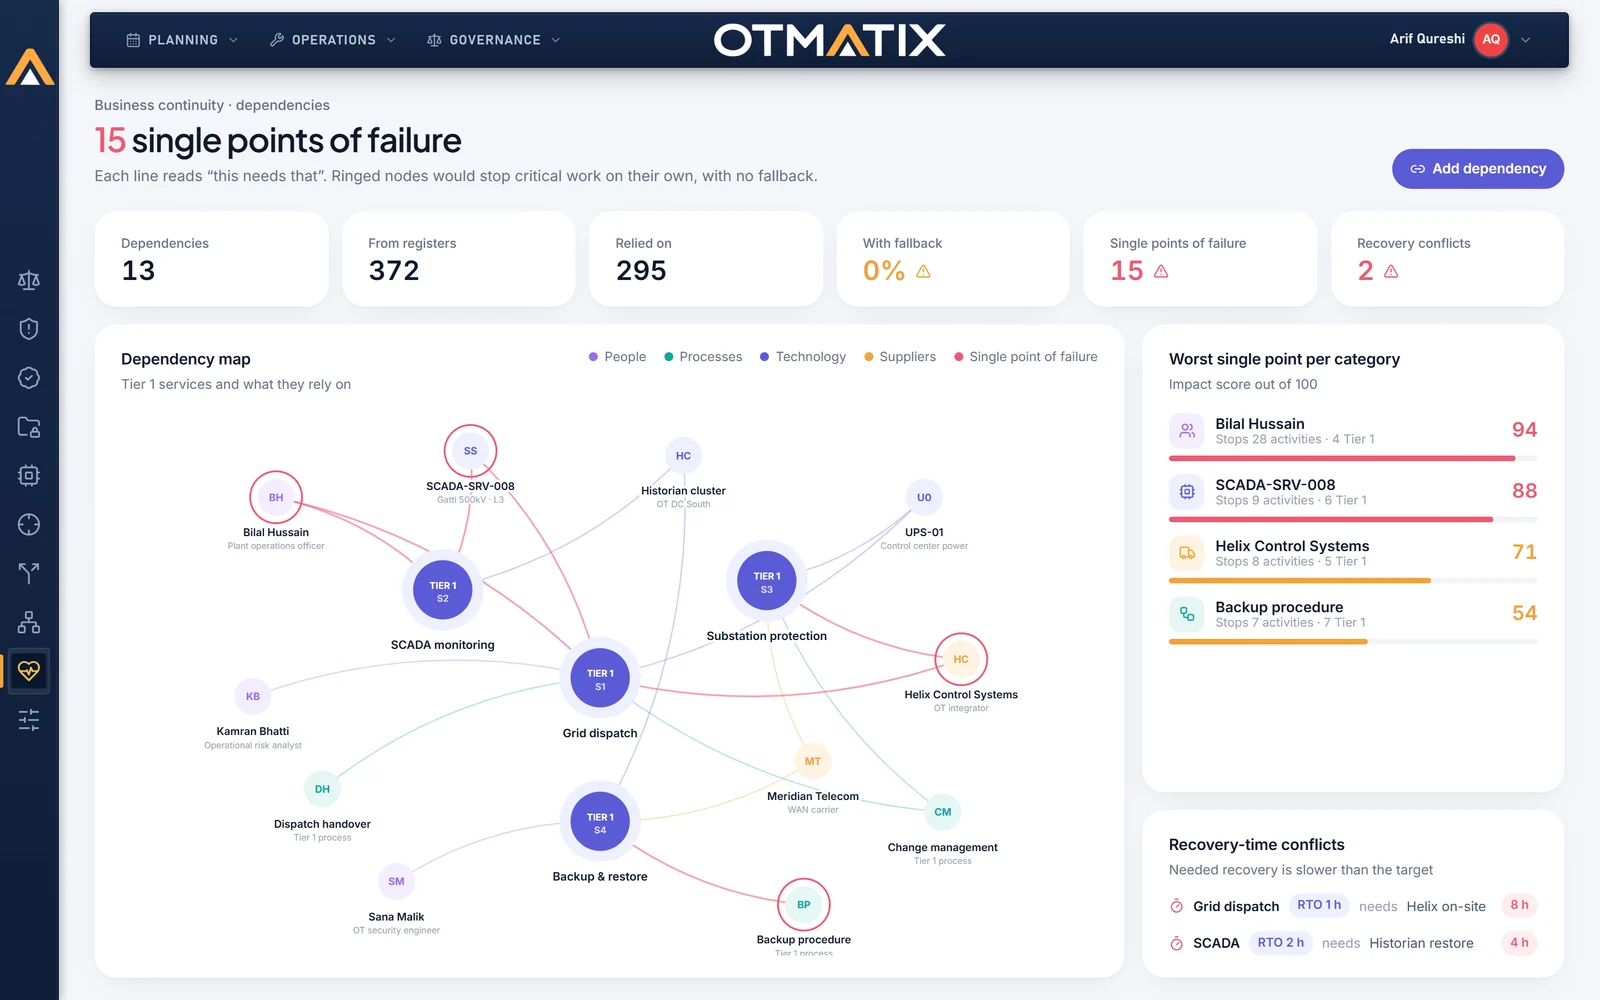
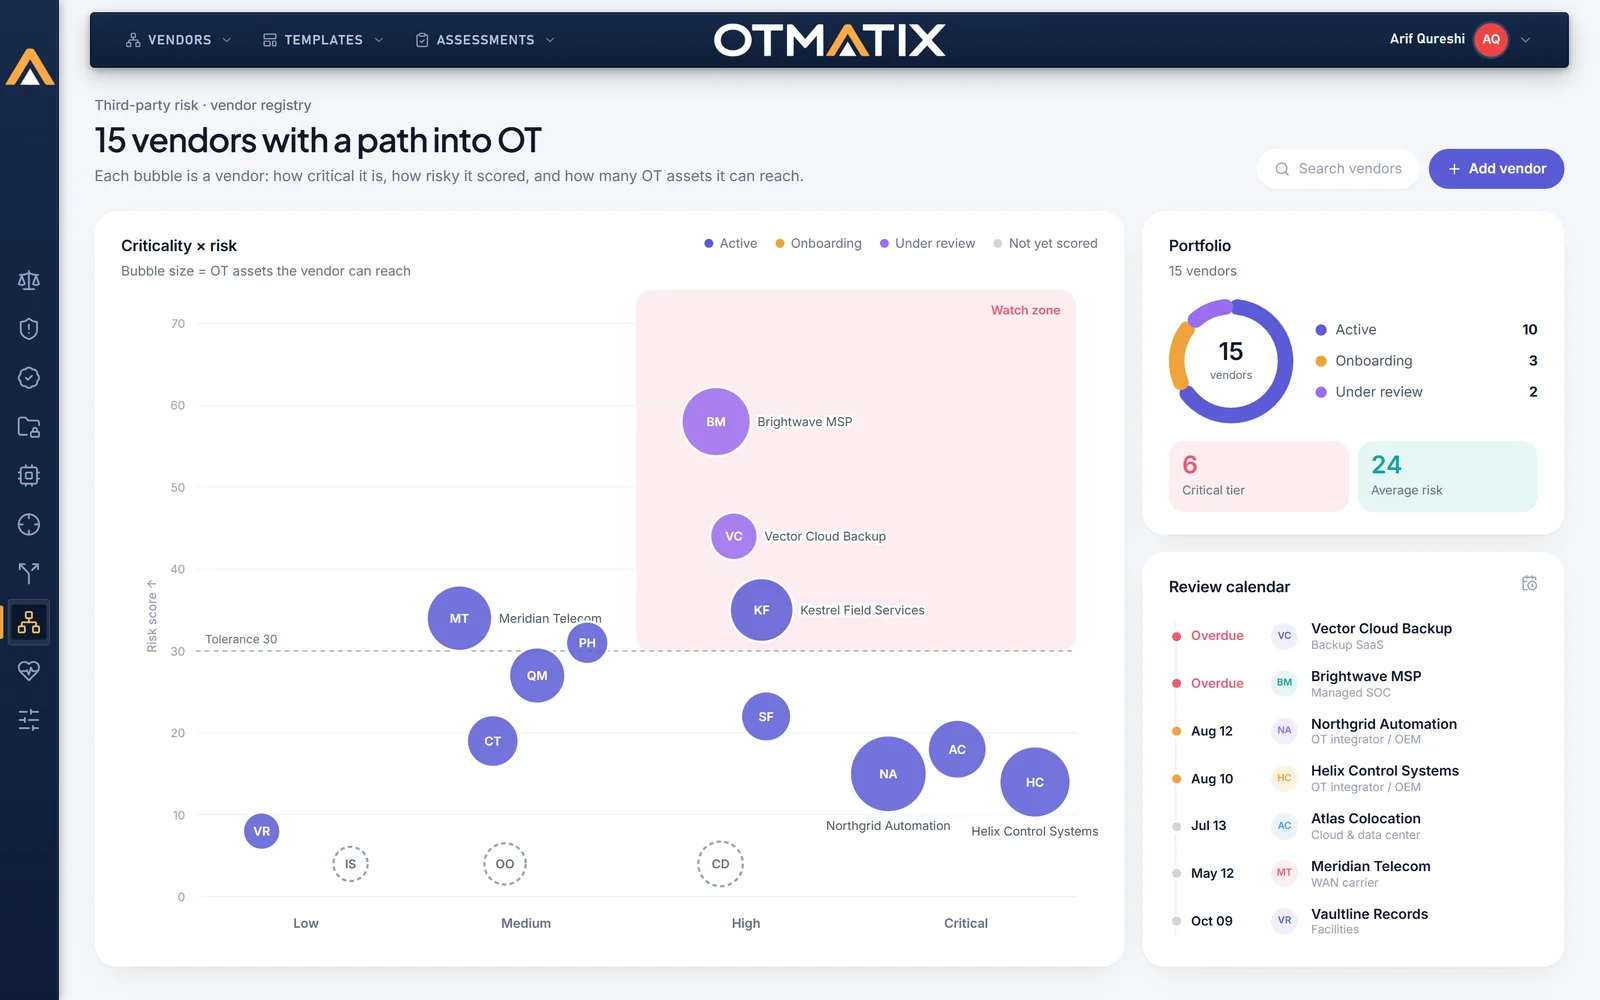
The OT security platform where every engagement we run lives. Asset level by design, so the evidence, decisions and uplift stay with you.
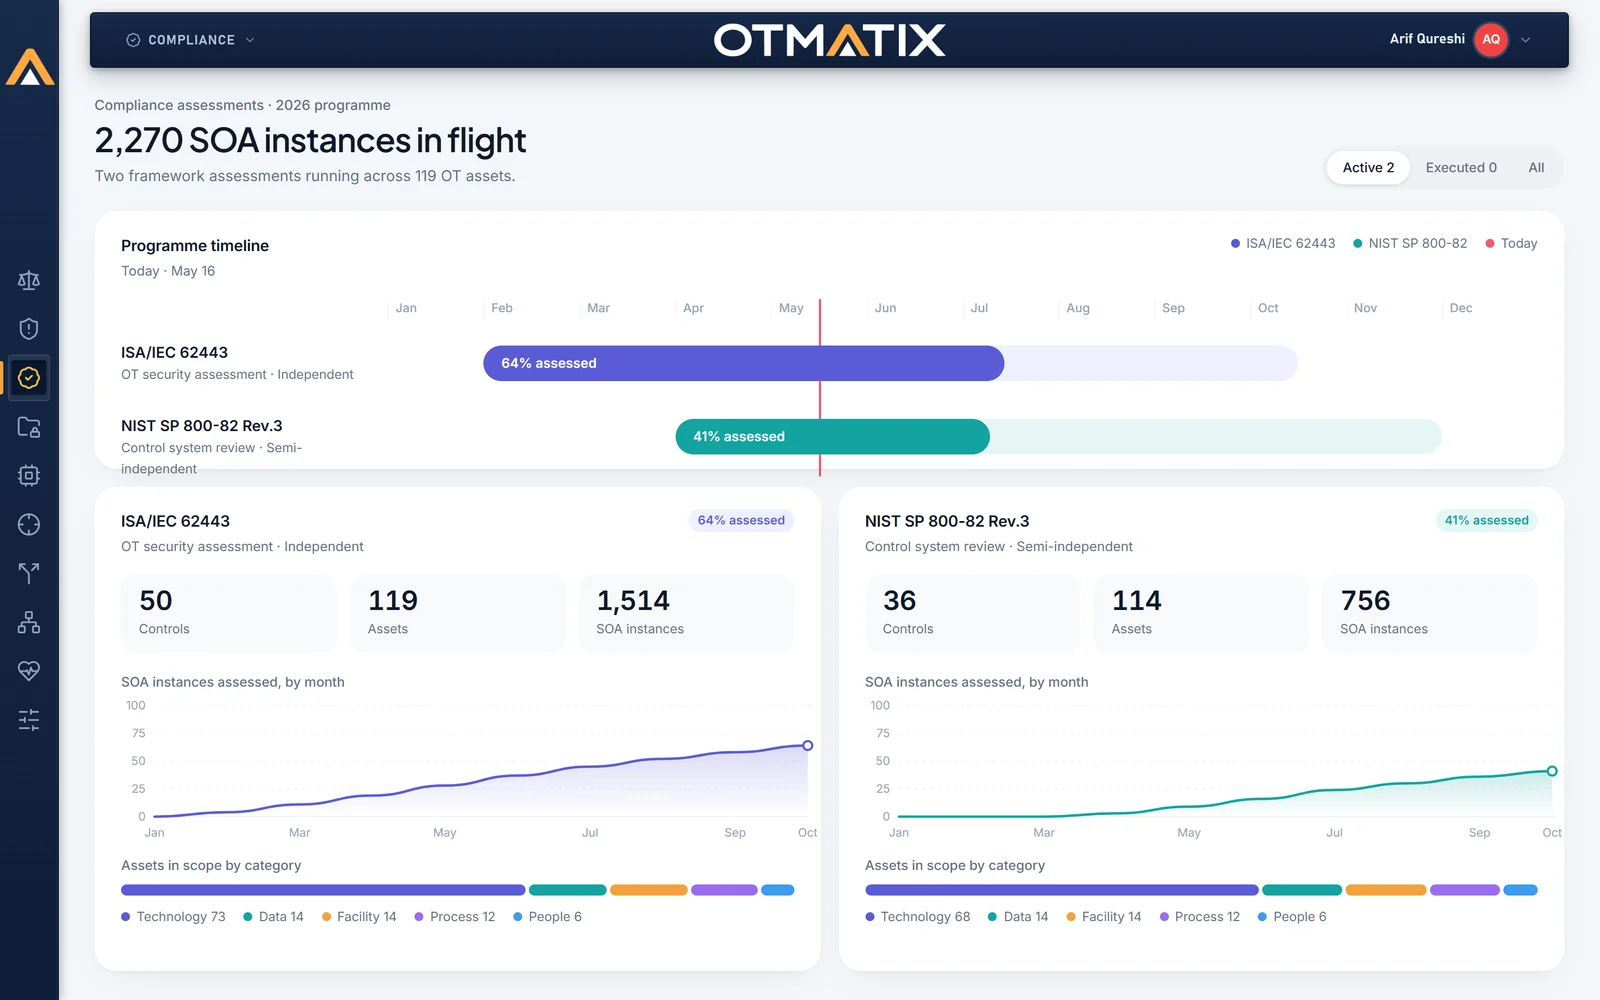
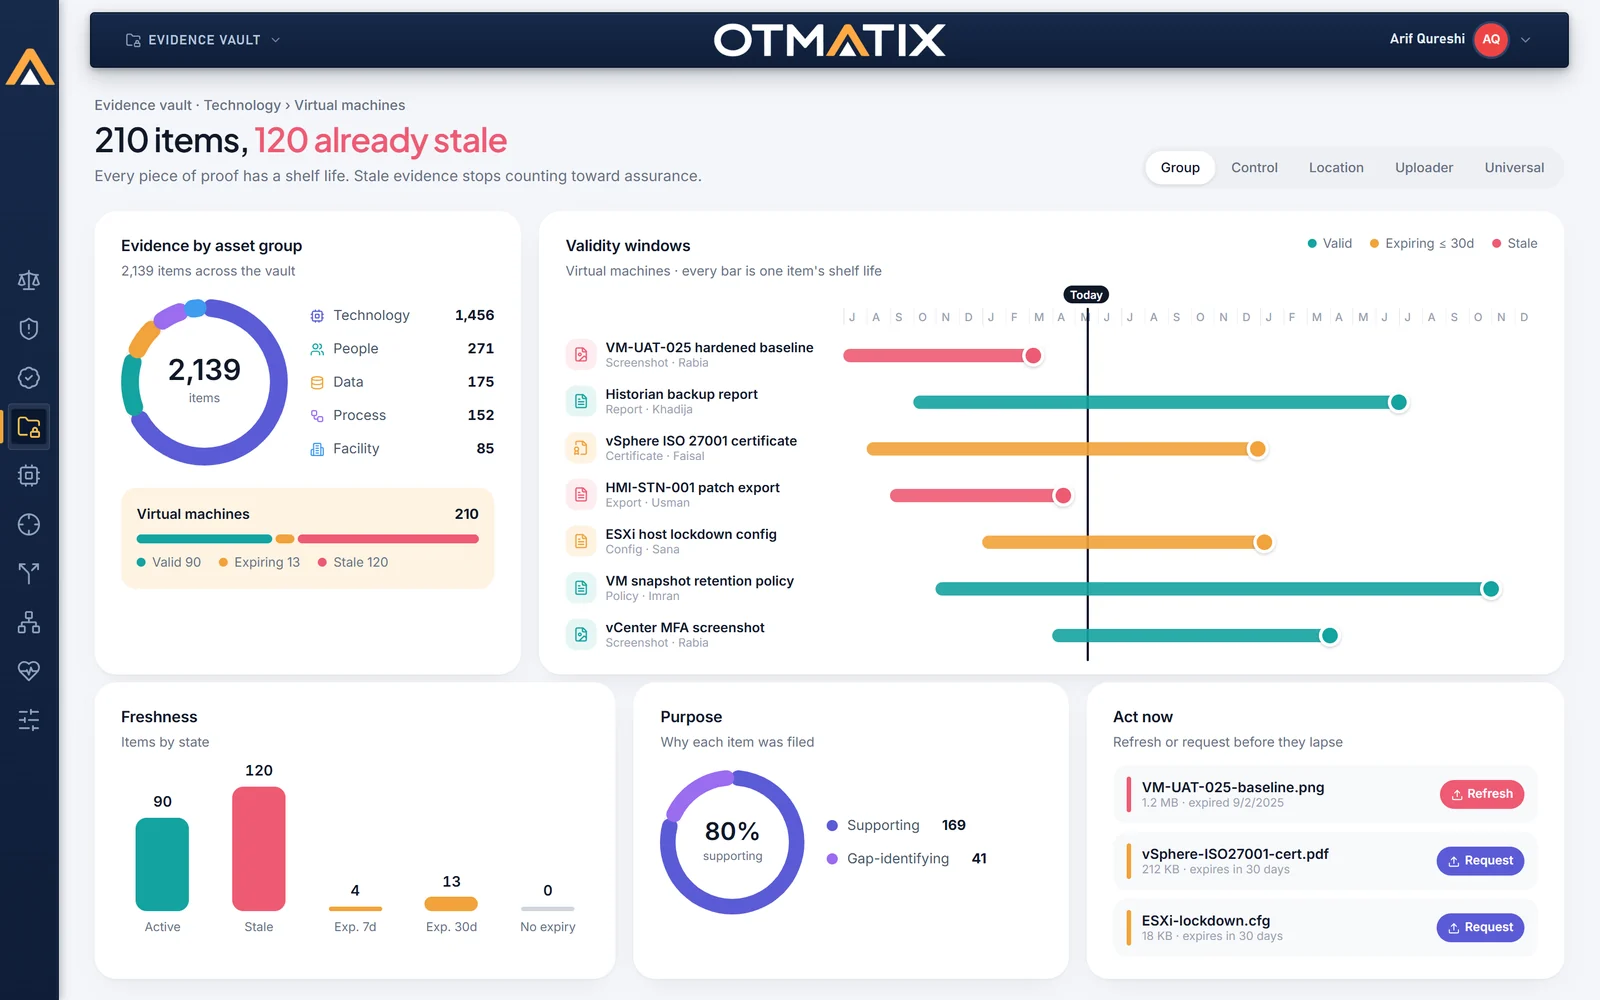
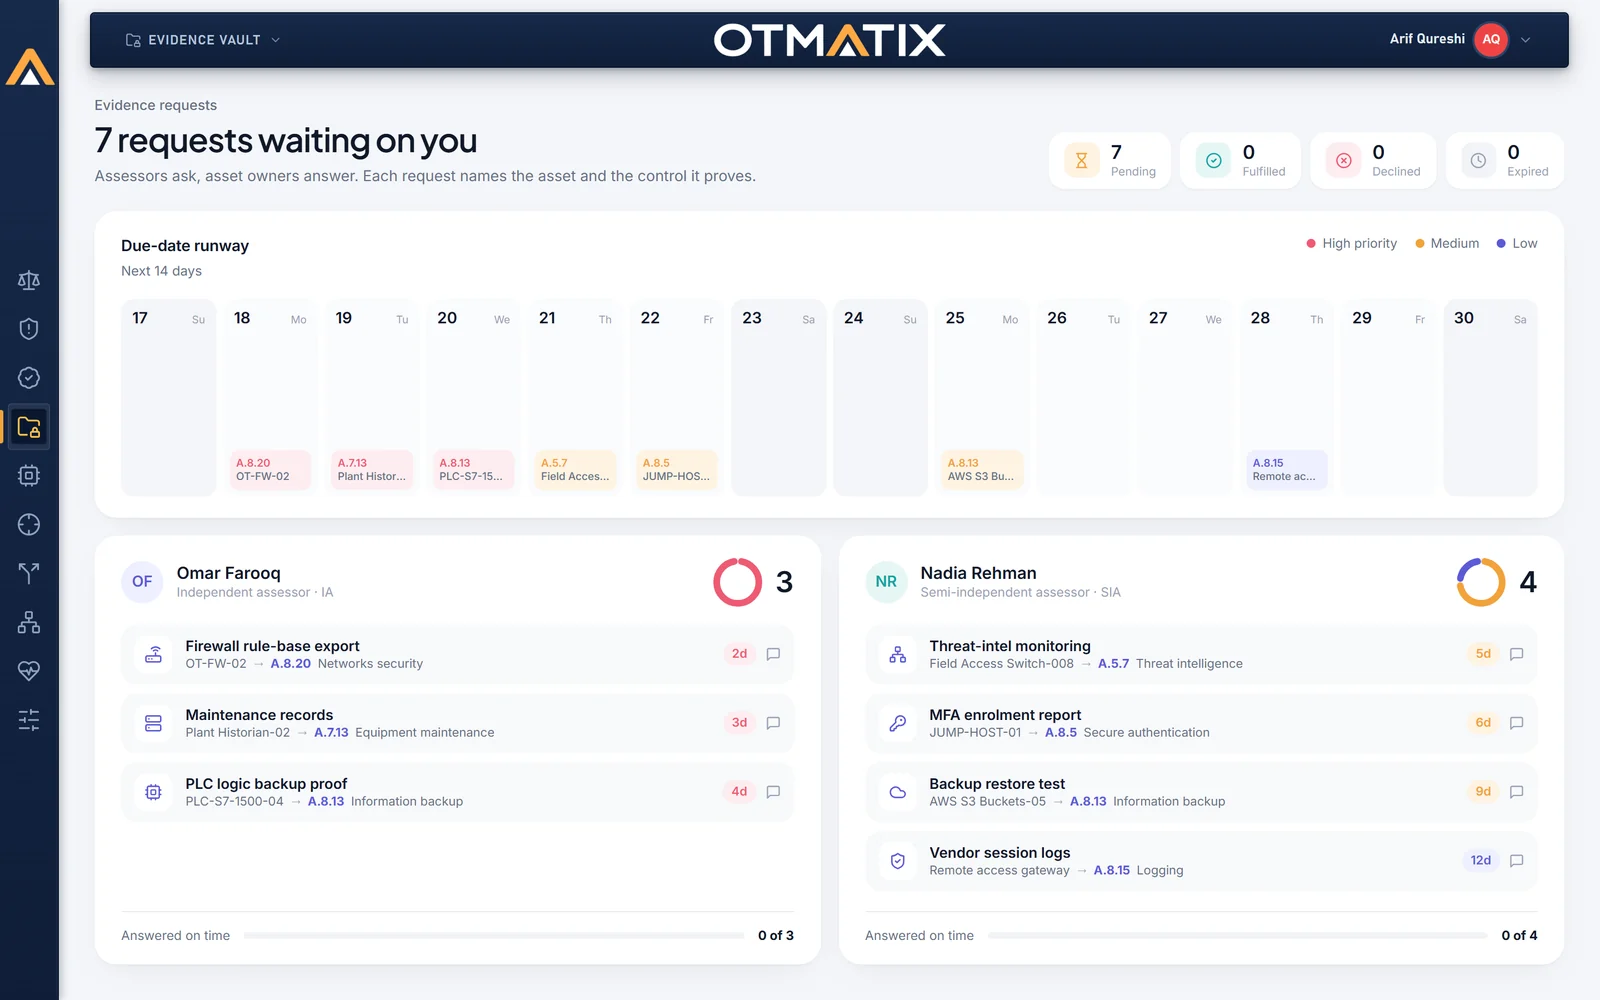
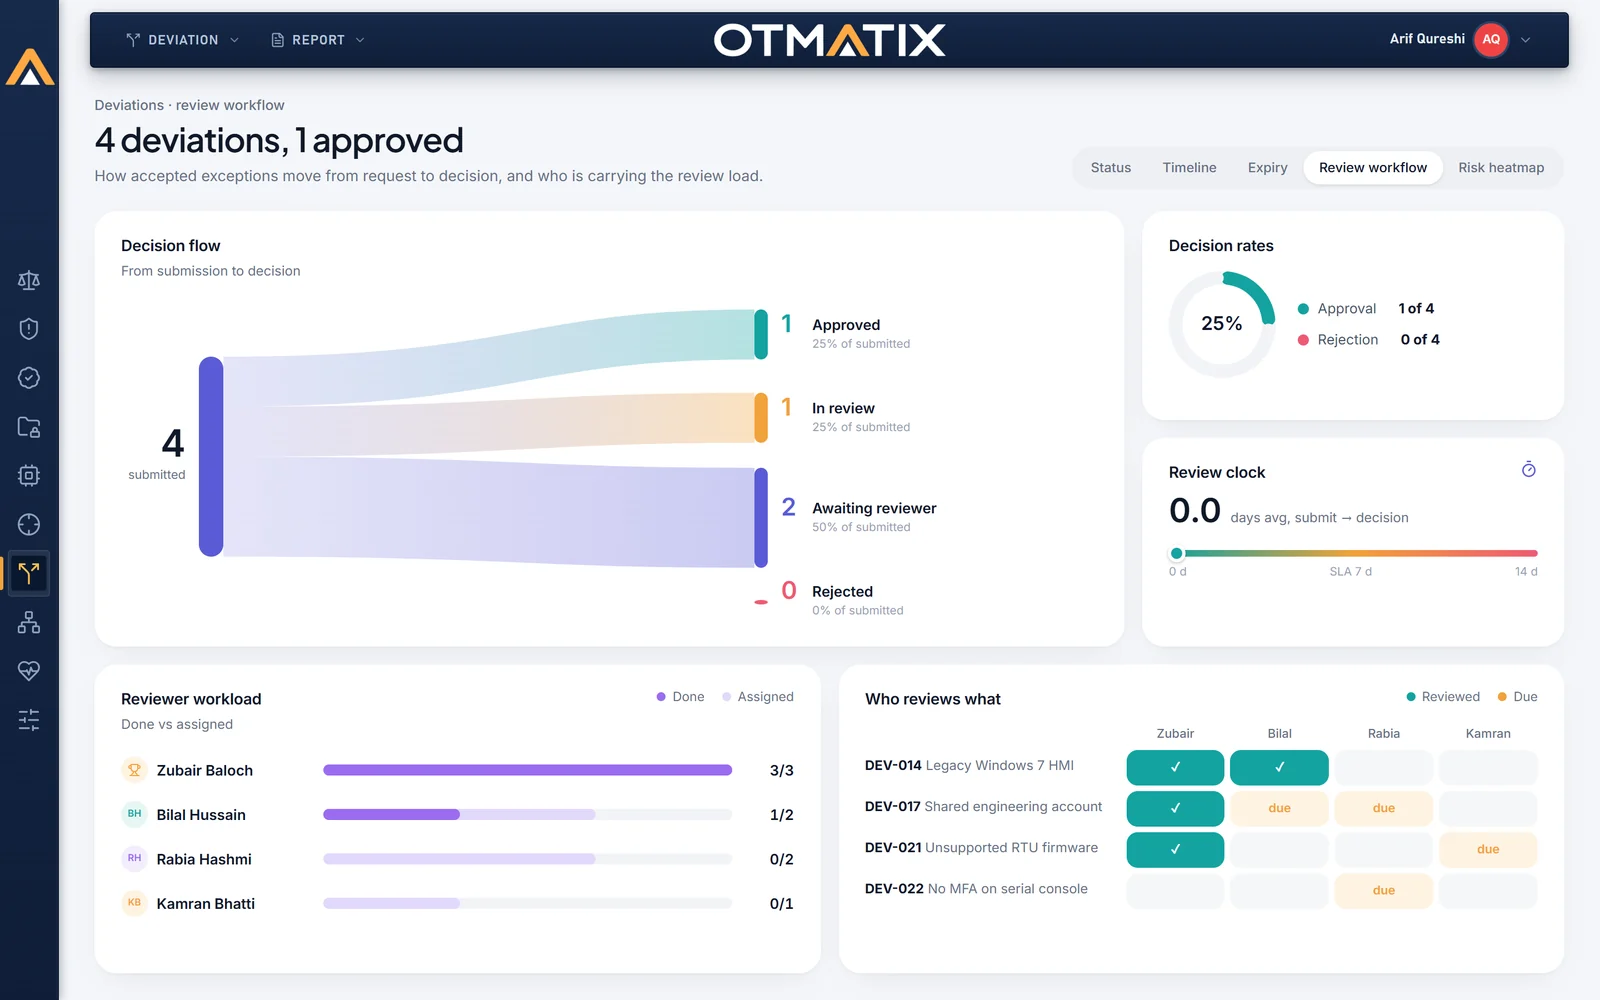
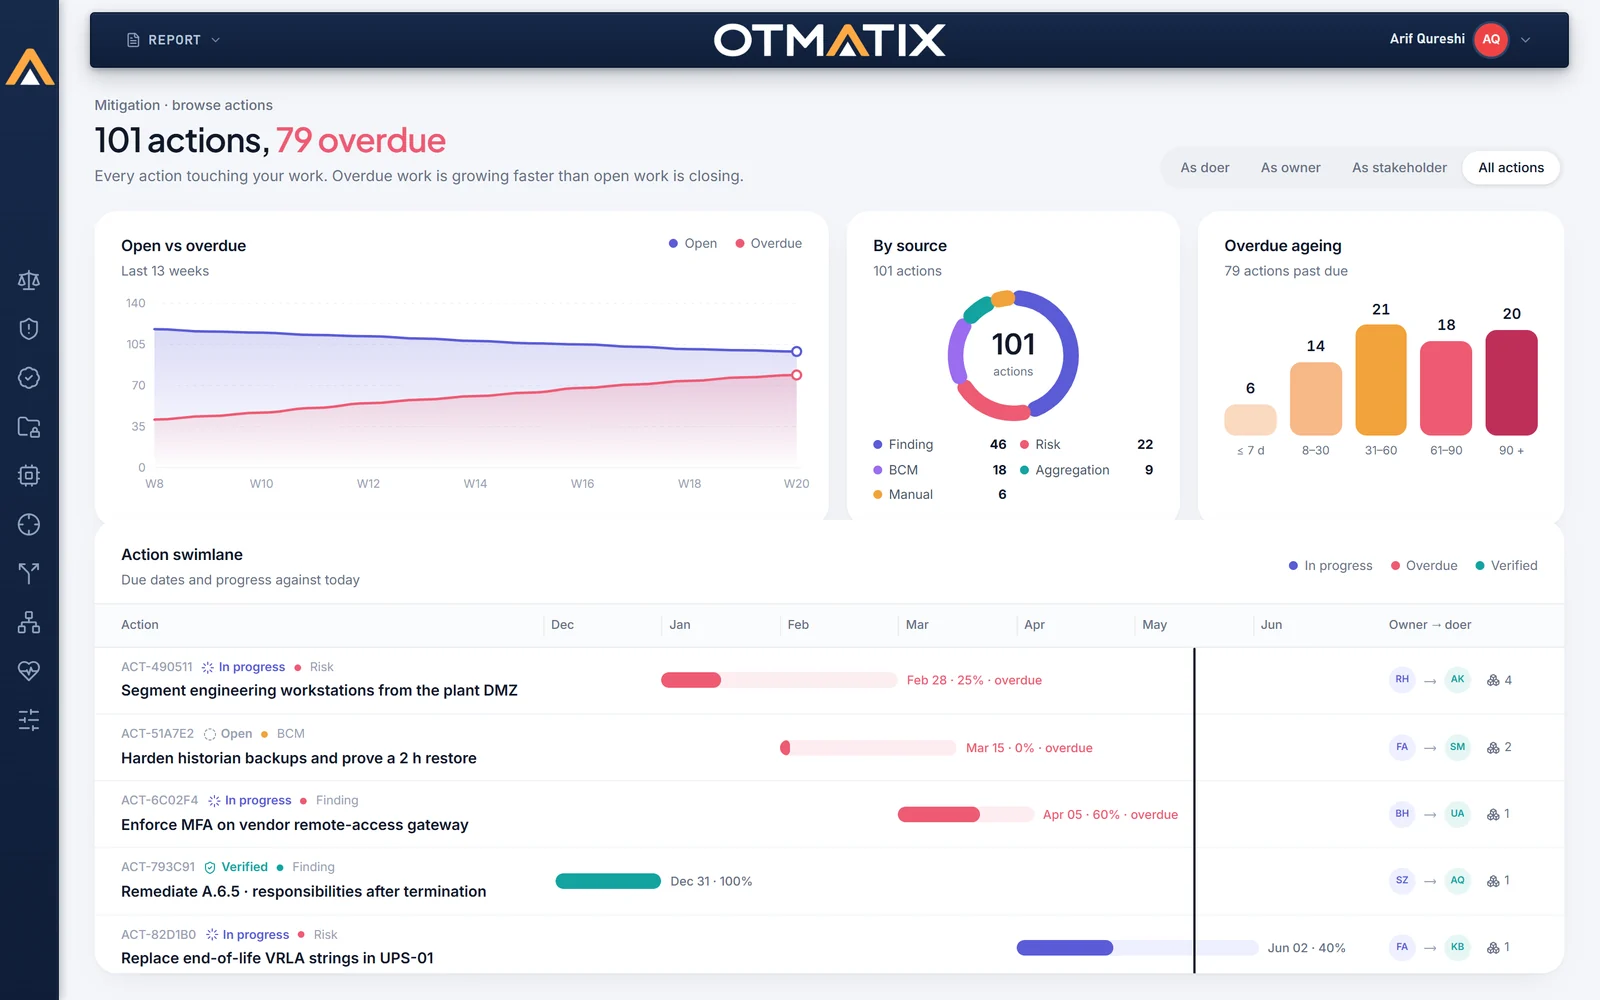
One partner. Three ways to run it.
The whole journey under one multi-year agreement, one governance cadence and one evidence trail in OTMATIX. Authority and approvals always stay with you. Pick the model that fits.
Senior practitioners run the programme with you inside OTMATIX, anchored by a Virtual OT CISO. You retain authority and approval rights; the programme never stalls when your team is stretched.
Measured against the standards that govern OT.
- 2-1Security programme and CSMS
- 2-4Service provider requirements
- 3-2Risk assessment, zones and conduits
- 3-3System security requirements and SLs
- 4-1Secure product development lifecycle
- 4-2Technical requirements for components
The principles we work by.
Headquartered in Sydney. On site where you are.
Senior practitioners across Australia, the United Kingdom, Ireland, Canada, the Gulf and South Asia.
Let’s secure every layer of your plant.
Begin with an OT Security Posture Assessment and ThePlantWalk. An evidenced view of your OT risk, and a clear path to the level of security you choose to hold.